AWS Security Blog
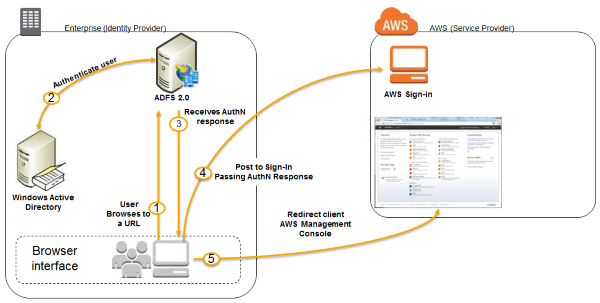
How to Set Up Uninterrupted, Federated User Access to AWS Using AD FS
Microsoft Active Directory Federation Services (AD FS) is a common identity provider that many AWS customers use to give federated users access to the AWS Management Console. AD FS uses multiple certificates to ensure secure communication between servers and to act as authentication mechanisms. One such mechanism is called the token-signing certificate. When the token-signing certificate expires, […]

How to Reduce Security Threats and Operating Costs Using AWS WAF and Amazon CloudFront
Note from July 3, 2017: The solution in this post has been integrated into AWS WAF Security Automations, and AWS maintains up-to-date solution code in the companion GitHub repository. Some Internet operations trust that clients are “well behaved.” As an operator of a publicly accessible web application, for example, you have to trust that the clients […]

Announcing Industry Best Practices for Securing AWS Resources
Today, we are happy to announce that the Center for Internet Security (CIS) has published the CIS AWS Foundations Benchmark, a set of security configuration best practices for AWS. These industry-accepted best practices go beyond the high-level security guidance already available, providing AWS users with clear, step-by-step implementation and assessment procedures. This is the first […]

How to Use AWS WAF to Block IP Addresses That Generate Bad Requests
Note from July 3, 2017: The solution in this post has been integrated into AWS WAF Security Automations, and AWS maintains up-to-date solution code in the companion GitHub repository. Internet-facing web applications are frequently scanned and probed by various sources, sometimes for good and other times to identify weaknesses. It takes some sleuthing to determine the […]

How to Use AWS Config to Help with Required HIPAA Audit Controls: Part 4 of the Automating HIPAA Compliance Series
In my previous posts in this series, I explained how to get started with the DevSecOps environment for HIPAA that is depicted in the following architecture diagram. In my second post in this series, I gave you guidance about how to set up AWS Service Catalog (#4 in the following diagram) to allow developers a […]

How to Configure Rate-Based Blacklisting with AWS WAF and AWS Lambda
Note from July 3, 2017: The solution in this post has been integrated into AWS WAF Security Automations, and AWS maintains up-to-date solution code in the companion GitHub repository. One security challenge you may have faced is how to prevent your web servers from being flooded by unwanted requests, or scanning tools such as bots and […]

How to Set Up DNS Resolution Between On-Premises Networks and AWS Using AWS Directory Service and Microsoft Active Directory
In my previous post, I showed how to use Simple AD to forward DNS requests originating from on-premises networks to an Amazon Route 53 private hosted zone. Today, I will show how you can use Microsoft Active Directory (also provisioned with AWS Directory Service) to provide the same DNS resolution with some additional forwarding capabilities. […]

How to Set Up DNS Resolution Between On-Premises Networks and AWS Using AWS Directory Service and Amazon Route 53
As you establish private connectivity between your on-premises networks and your AWS Virtual Private Cloud (VPC) environments, the need for Domain Name System (DNS) resolution across these environments grows in importance. One common approach used to address this need is to run DNS servers on Amazon EC2 across multiple Availability Zones (AZs) and integrate them […]

How to Help Protect Sensitive Data with AWS KMS
August 31, 2021: AWS KMS is replacing the term customer master key (CMK) with AWS KMS key and KMS key. The concept has not changed. To prevent breaking changes, AWS KMS is keeping some variations of this term. More info. AWS Key Management Service (AWS KMS) celebrated its one-year launch anniversary in November 2015, and […]

How to Record and Govern Your IAM Resource Configurations Using AWS Config
AWS Config recently added the ability to record changes to the configuration of your AWS Identity and Access Management (IAM) users, groups, and roles (collectively referred to as IAM entities) and the policies associated with them. Using this feature, you can record configuration details for these IAM entities, including details about which policies are associated […]