AWS Security Blog

Easily Replace or Attach an IAM Role to an Existing EC2 Instance by Using the EC2 Console
April 13, 2022: This blog is out of date. Please refer to this documentation for updated info: Amazon Elastic Compute Cloud User Guide AWS Identity and Access Management (IAM) roles enable your applications running on Amazon EC2 to use temporary security credentials. IAM roles for EC2 make it easier for your applications to make API […]

How to Audit Your AWS Resources for Security Compliance by Using Custom AWS Config Rules
AWS Config Rules enables you to implement security policies as code for your organization and evaluate configuration changes to AWS resources against these policies. You can use Config rules to audit your use of AWS resources for compliance with external compliance frameworks such as CIS AWS Foundations Benchmark and with your internal security policies related […]

AWS Announces CISPE Membership and Compliance with First-Ever Code of Conduct for Data Protection in the Cloud
September 7, 2023: We updated the CISPE Code of Conduct link. Please refer to this page for the updated info: CISPE Code of Conduct I have two exciting announcements today, both showing AWS’s continued commitment to ensuring that customers can comply with EU Data Protection requirements when using our services. AWS and CISPE First, I’m […]

How to Enable Multi-Factor Authentication for AWS Services by Using AWS Microsoft AD and On-Premises Credentials
You can now enable multi-factor authentication (MFA) for users of AWS services such as Amazon WorkSpaces and Amazon QuickSight and their on-premises credentials by using your AWS Directory Service for Microsoft Active Directory directory, also known as AWS Microsoft AD. MFA adds an extra layer of protection to a user name and password (the first “factor”) […]

How to Easily Log On to AWS Services by Using Your On-Premises Active Directory
AWS Directory Service for Microsoft Active Directory (Enterprise Edition), also known as Microsoft AD, now enables your users to log on with just their on-premises Active Directory (AD) user name—no domain name is required. This new domainless logon feature makes it easier to set up connections to your on-premises AD for use with applications such […]

New! Attach an AWS IAM Role to an Existing Amazon EC2 Instance by Using the AWS CLI
AWS Identity and Access Management (IAM) roles enable your applications running on Amazon EC2 to use temporary security credentials that AWS creates, distributes, and rotates automatically. Using temporary credentials is an IAM best practice because you do not need to maintain long-term keys on your instance. Using IAM roles for EC2 also eliminates the need […]

How to Remediate Amazon Inspector Security Findings Automatically
May 31, 2022: The updated blog post is available here. June 18, 2020: This solution no longer works, and the Lambda runtime this code is relying on has been deprecated. When we have an updated blog, we’ll add a link to it here. Updated on November 27, 2018: We added a policy to the instructions […]
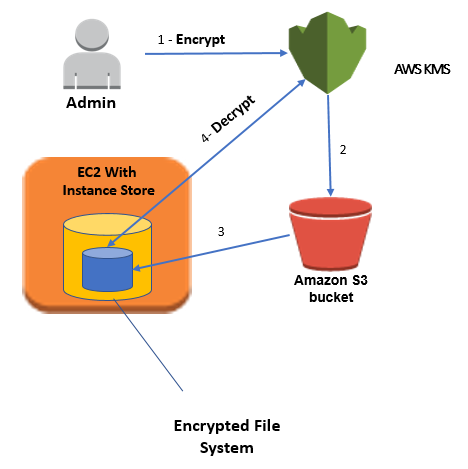
How to Protect Data at Rest with Amazon EC2 Instance Store Encryption
April 25, 2023: We’ve updated this blog post to include more security learning resources. Note: By default, an instance type that includes an NVMe instance store encrypts data at rest using an XTS-AES-256 block cipher. See this FAQ about NVMe-supported instance types. If you’re using an NVMw instance type, then data at rest is encrypted […]

How to Detect and Automatically Remediate Unintended Permissions in Amazon S3 Object ACLs with CloudWatch Events
Update on October 24, 2018: Note that if you do not author the Lambda function correctly, this setup can create an infinite loop (in this case, a rule that is fired repeatedly, which can impact your AWS resources and cause higher than expected charges to your account). The example Lambda function I provide in Step […]

New SOC 2 Report Available: Confidentiality
As with everything at Amazon, the success of our security and compliance program is primarily measured by one thing: our customers’ success. Our customers drive our portfolio of compliance reports, attestations, and certifications that support their efforts in running a secure and compliant cloud environment. As a result of our engagement with key customers across […]