AWS Security Blog
Validate access to your S3 buckets before deploying permissions changes with IAM Access Analyzer
AWS Identity and Access Management (IAM) Access Analyzer helps you monitor and reduce access by using automated reasoning to generate comprehensive findings for resource access. Now, you can preview and validate public and cross-account access before deploying permission changes. For example, you can validate whether your S3 bucket would allow public access before deploying your […]

How to replicate secrets in AWS Secrets Manager to multiple Regions
On March 3, 2021, we launched a new feature for AWS Secrets Manager that makes it possible for you to replicate secrets across multiple AWS Regions. You can give your multi-Region applications access to replicated secrets in the required Regions and rely on Secrets Manager to keep the replicas in sync with the primary secret. […]

C5 Type 2 attestation report now available with one new Region and 123 services in scope
Amazon Web Services (AWS) is pleased to announce the issuance of the 2020 Cloud Computing Compliance Controls Catalogue (C5) Type 2 attestation report. We added one new AWS Region (Europe-Milan) and 21 additional services and service features to the scope of the 2020 report. Germany’s national cybersecurity authority, Bundesamt für Sicherheit in der Informationstechnik (BSI), […]

How AWS IAM Identity Center Active Directory sync enhances AWS application experiences
September 12, 2022: This blog post has been updated to reflect the new name of AWS Single Sign-On (SSO) – AWS IAM Identity Center. Read more about the name change here. IAM Identity CenterIdentity management is easiest when you can manage identities in a centralized location and use these identities across various accounts and applications. […]

Essential security for everyone: Building a secure AWS foundation
August 10, 2022: This blog post has been updated to reflect the new name of AWS Single Sign-On (SSO) – AWS IAM Identity Center. Read more about the name change here. In this post, I will show you how teams of all sizes can gain access to world-class security in the cloud without a dedicated […]
Automate Amazon EC2 instance isolation by using tags
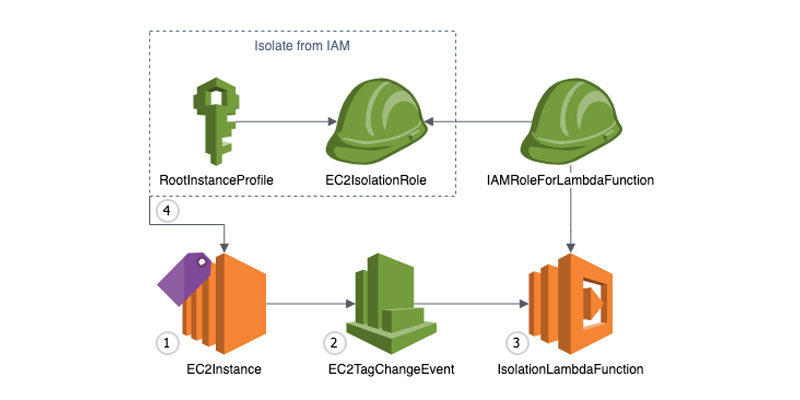
Containment is a crucial part of an overall Incident Response Strategy, as this practice allows time for responders to perform forensics, eradication and recovery during an Incident. There are many different approaches to containment. In this post, we will be focusing on isolation—the ability to keep multiple targets separated so that each target only sees […]

TLS 1.2 will be required for all AWS FIPS endpoints beginning March 31, 2021
November 10, 2022: This project was successfully completed in March 2021. TLS 1.2 is now the minimum version supported for all connections to AWS FIPS service endpoints. Note we will be implementing the same policy for non-FIPS endpoints by June 2023. If you also use these endpoints see https://usvm.9mmj.com/blogs/security/tls-1-2-required-for-aws-endpoints/ for details. To help you meet […]

How to protect sensitive data for its entire lifecycle in AWS
April 25, 2023: We’ve updated this blog post to include more security learning resources. Many Amazon Web Services (AWS) customer workflows require ingesting sensitive and regulated data such as Payments Card Industry (PCI) data, personally identifiable information (PII), and protected health information (PHI). In this post, I’ll show you a method designed to protect sensitive […]

How to set up a recurring Security Hub summary email
January 13, 2025: This post was updated to include code to create Security Hub custom insights through the use of CloudFormation. AWS Security Hub provides a comprehensive view of your security posture in Amazon Web Services (AWS) and helps you check your environment against security standards and best practices. In this post, we’ll show you […]

Updated whitepaper available: Encrypting File Data with Amazon Elastic File System
We’re sharing an update to the Encrypting File Data with Amazon Elastic File System whitepaper to provide customers with guidance on enforcing encryption of data at rest and in transit in Amazon Elastic File System (Amazon EFS). Amazon EFS provides simple, scalable, highly available, and highly durable shared file systems in the cloud. The file […]